TALK · · 31 SLIDES
Updated
Future of SecOps Tooling
A recap of my talk at SecOps Reset in Dublin April 2026, my hot takes on where security tooling is going.
Delivered at SecOps Reset in Dublin on 27 April 2026, at the Irish Architectural Archive on Merrion Square. Use the arrows or your keyboard to step through the deck.
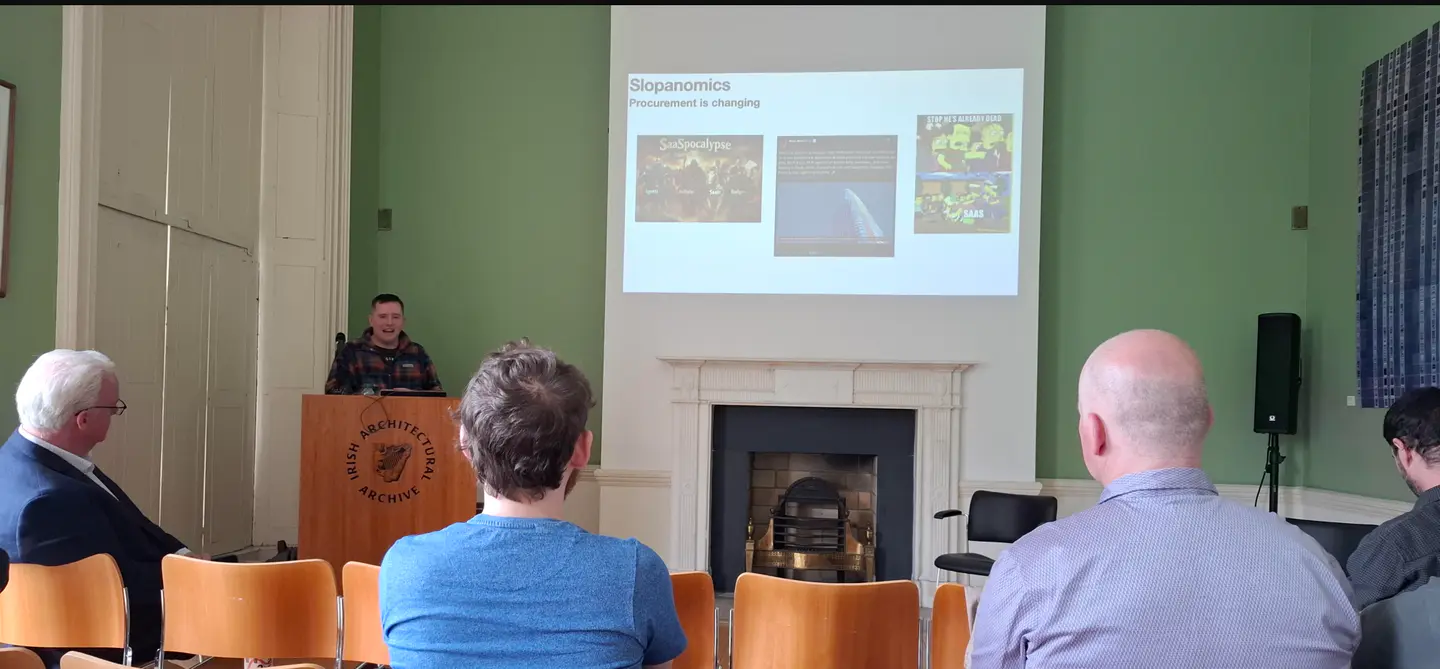
The Irish Architectural Archive on Merrion Square.
The talk
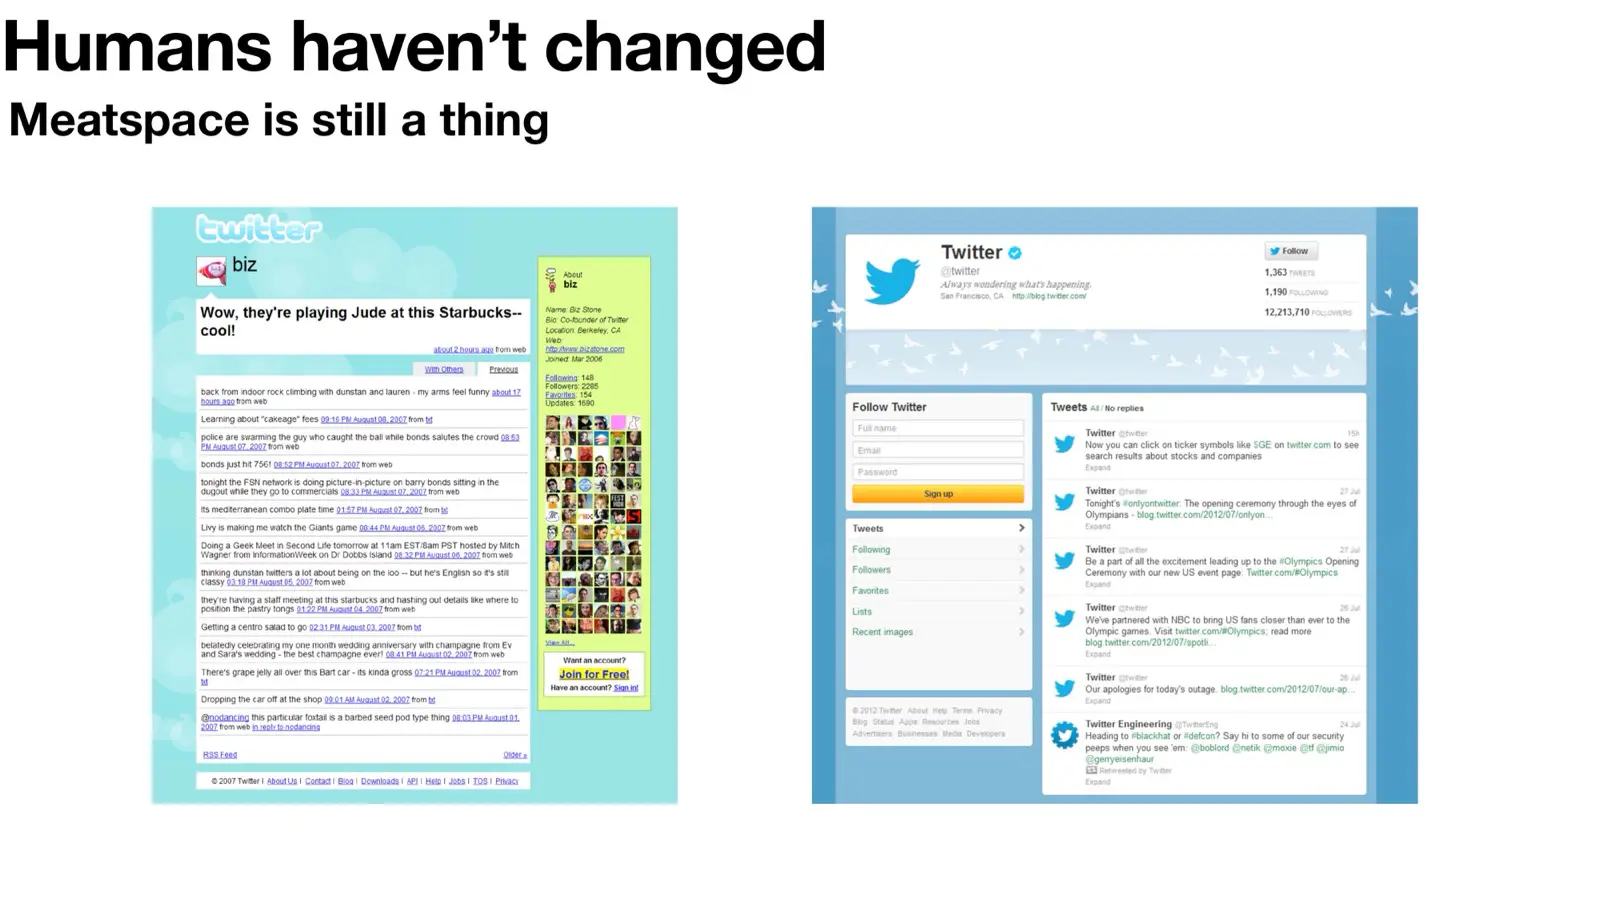
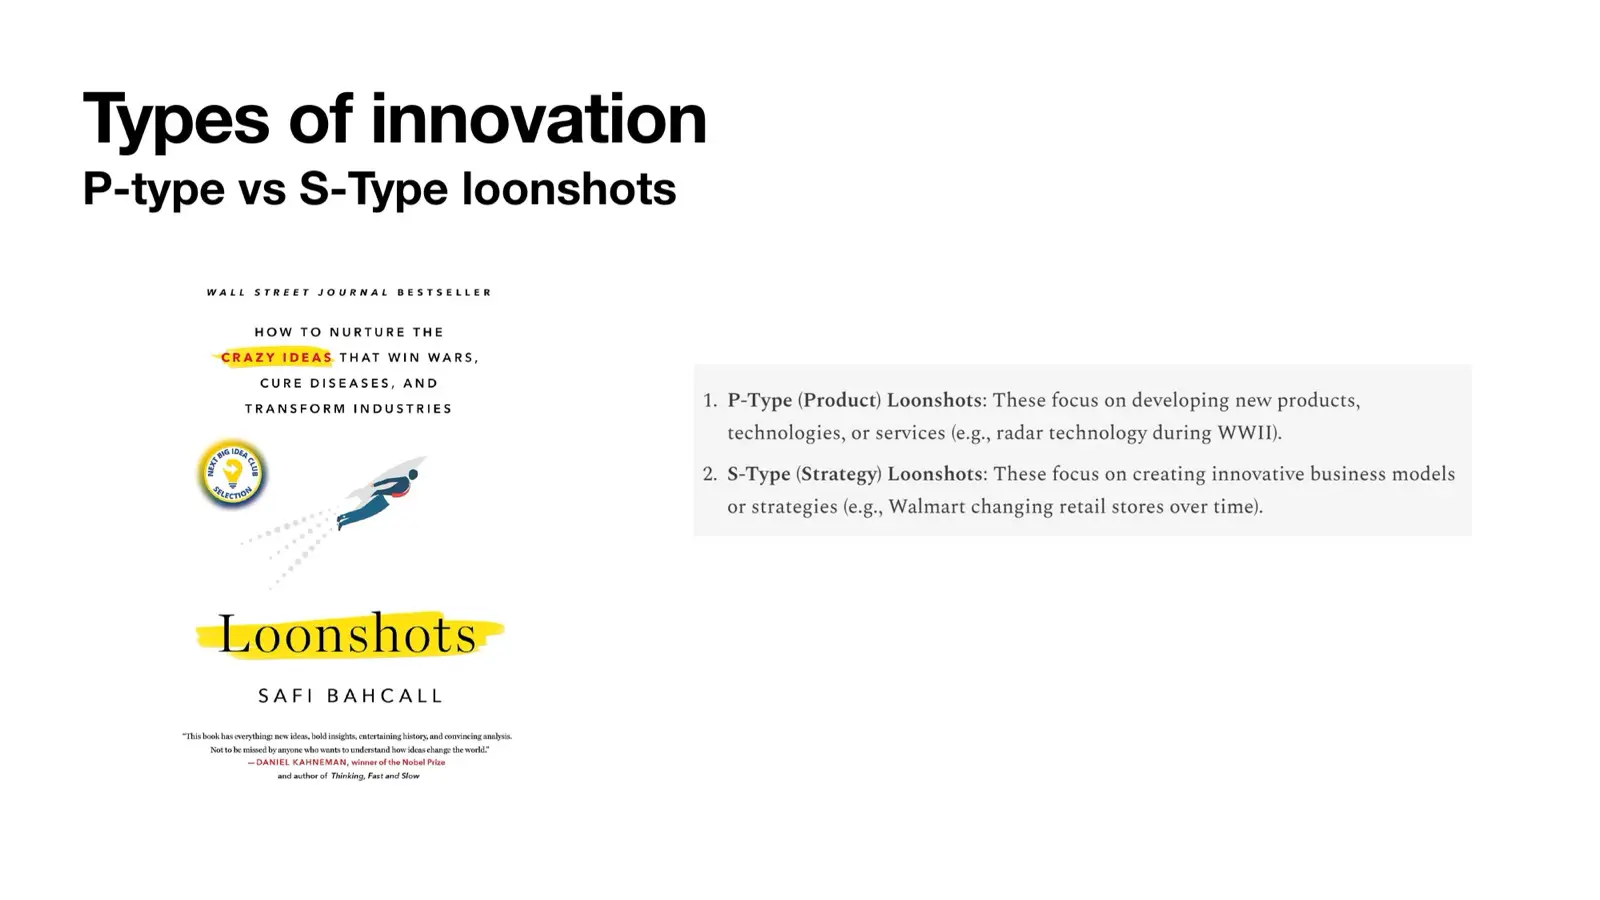
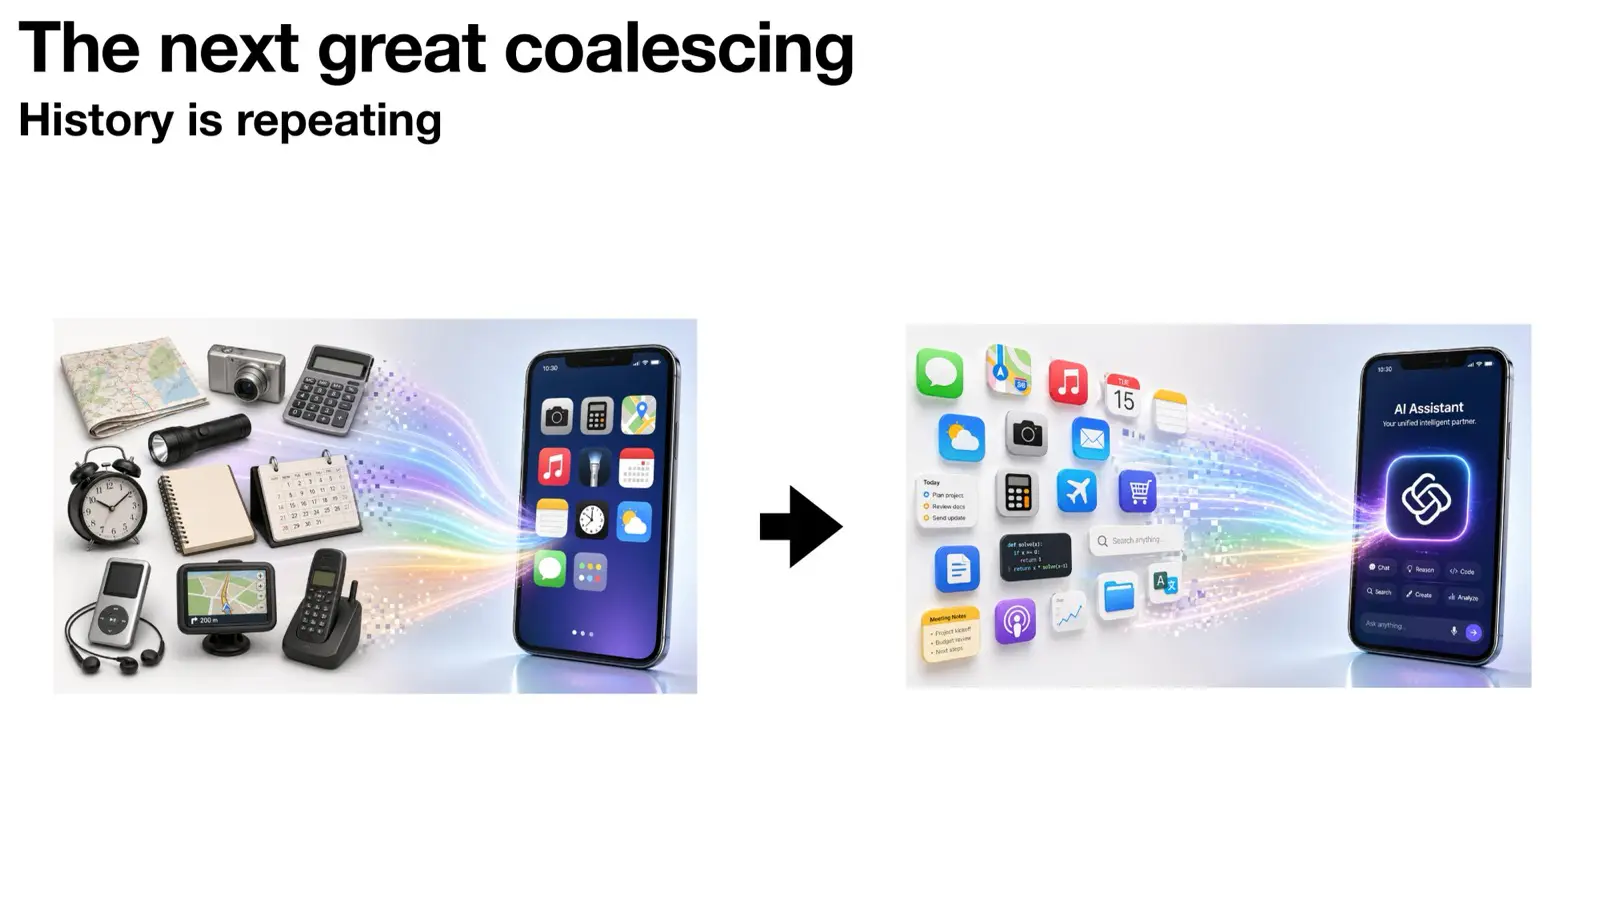
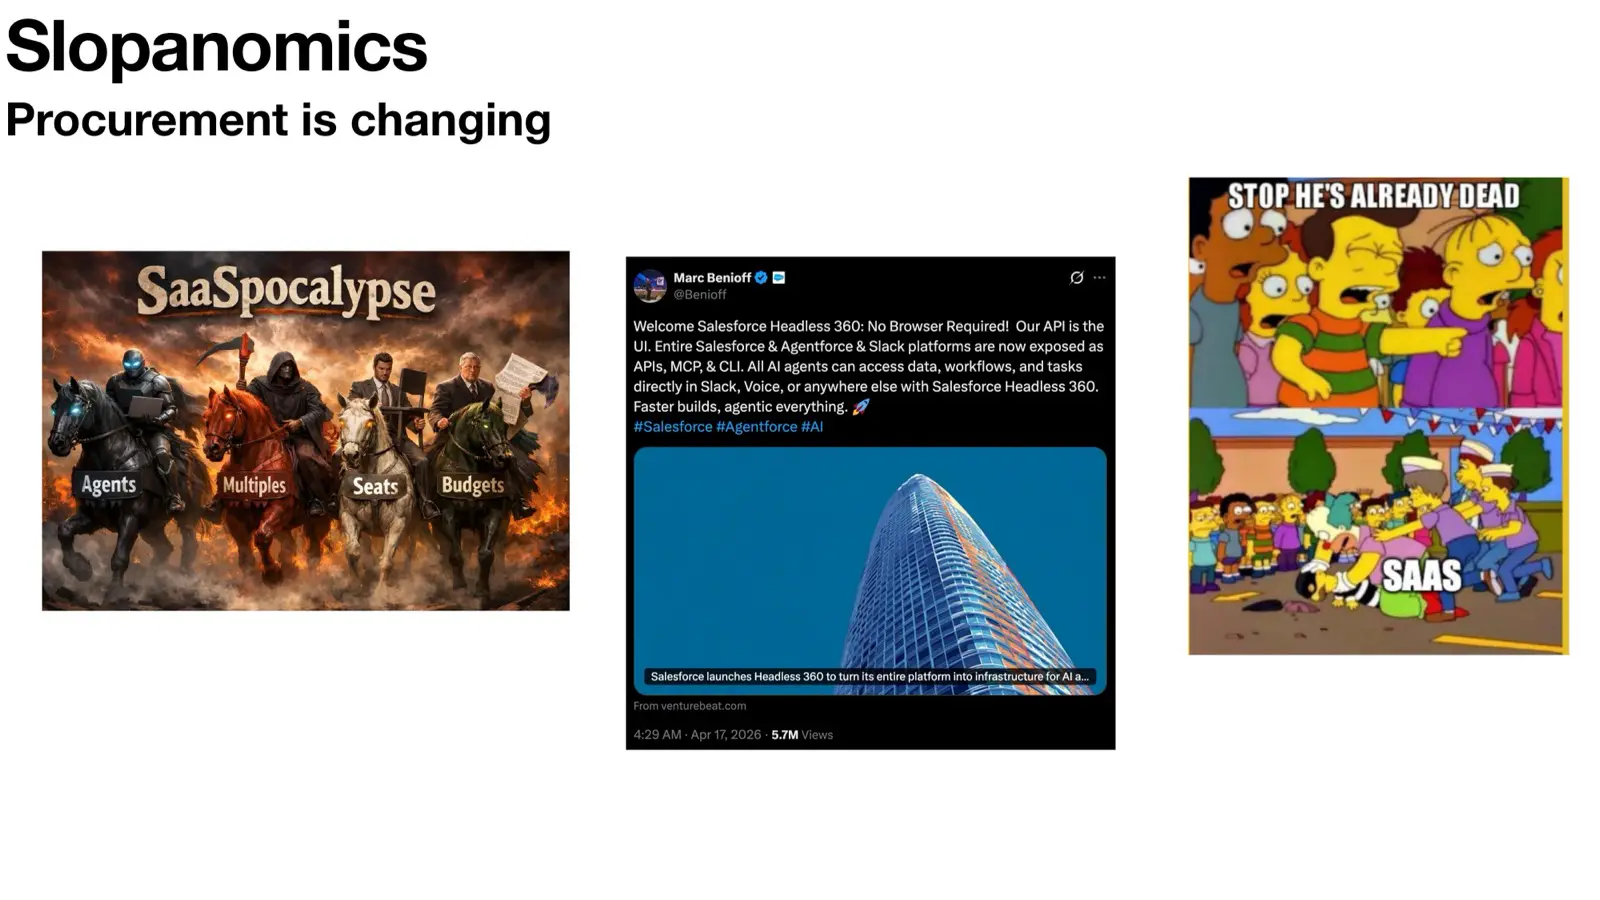
“Future of SecOps Tooling”, subtitled hot takes on tools. My argument was that most of what feels new in security tooling isn’t. A lot of it is old ideas coming back around, and the question worth asking is which of them AI finally makes worth building. I also spent a few slides arguing we should reinvent Clippy.
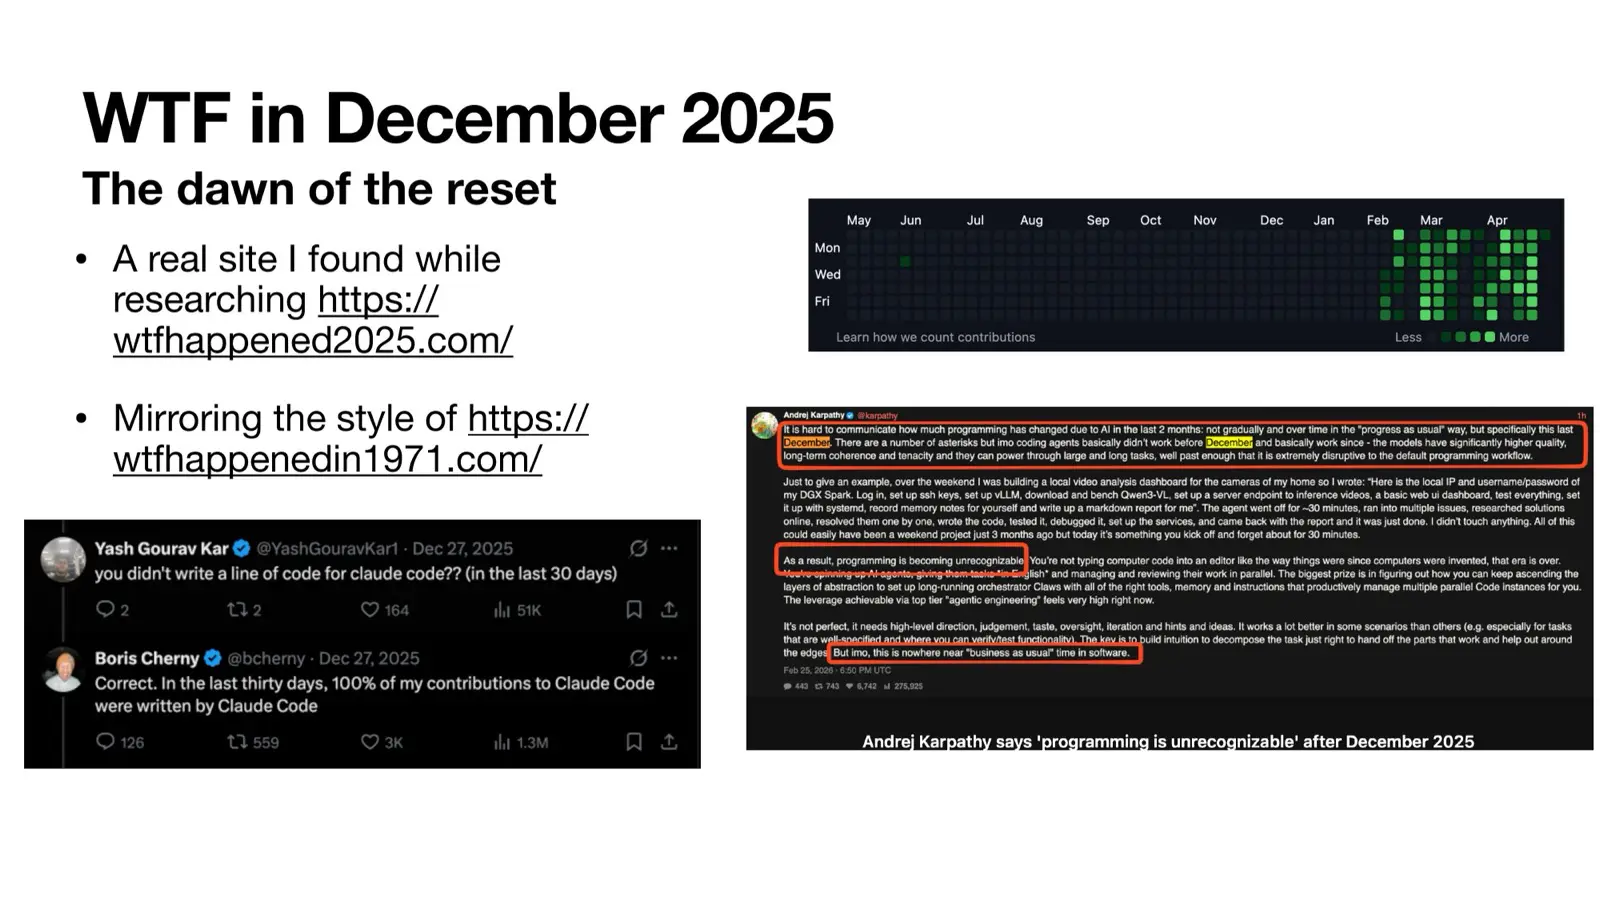
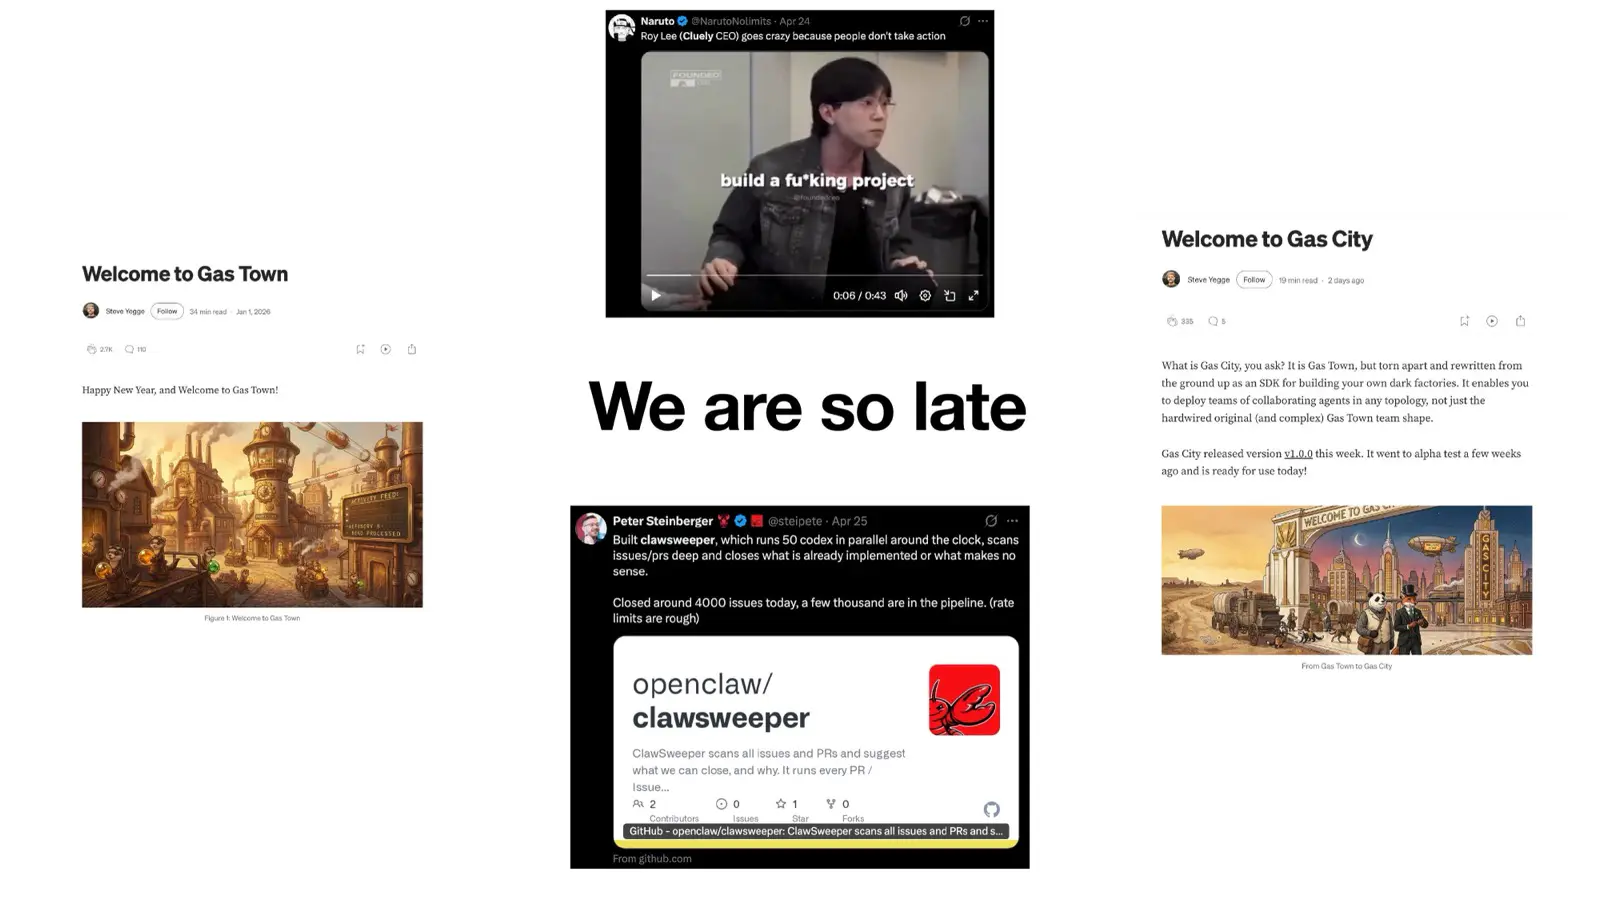
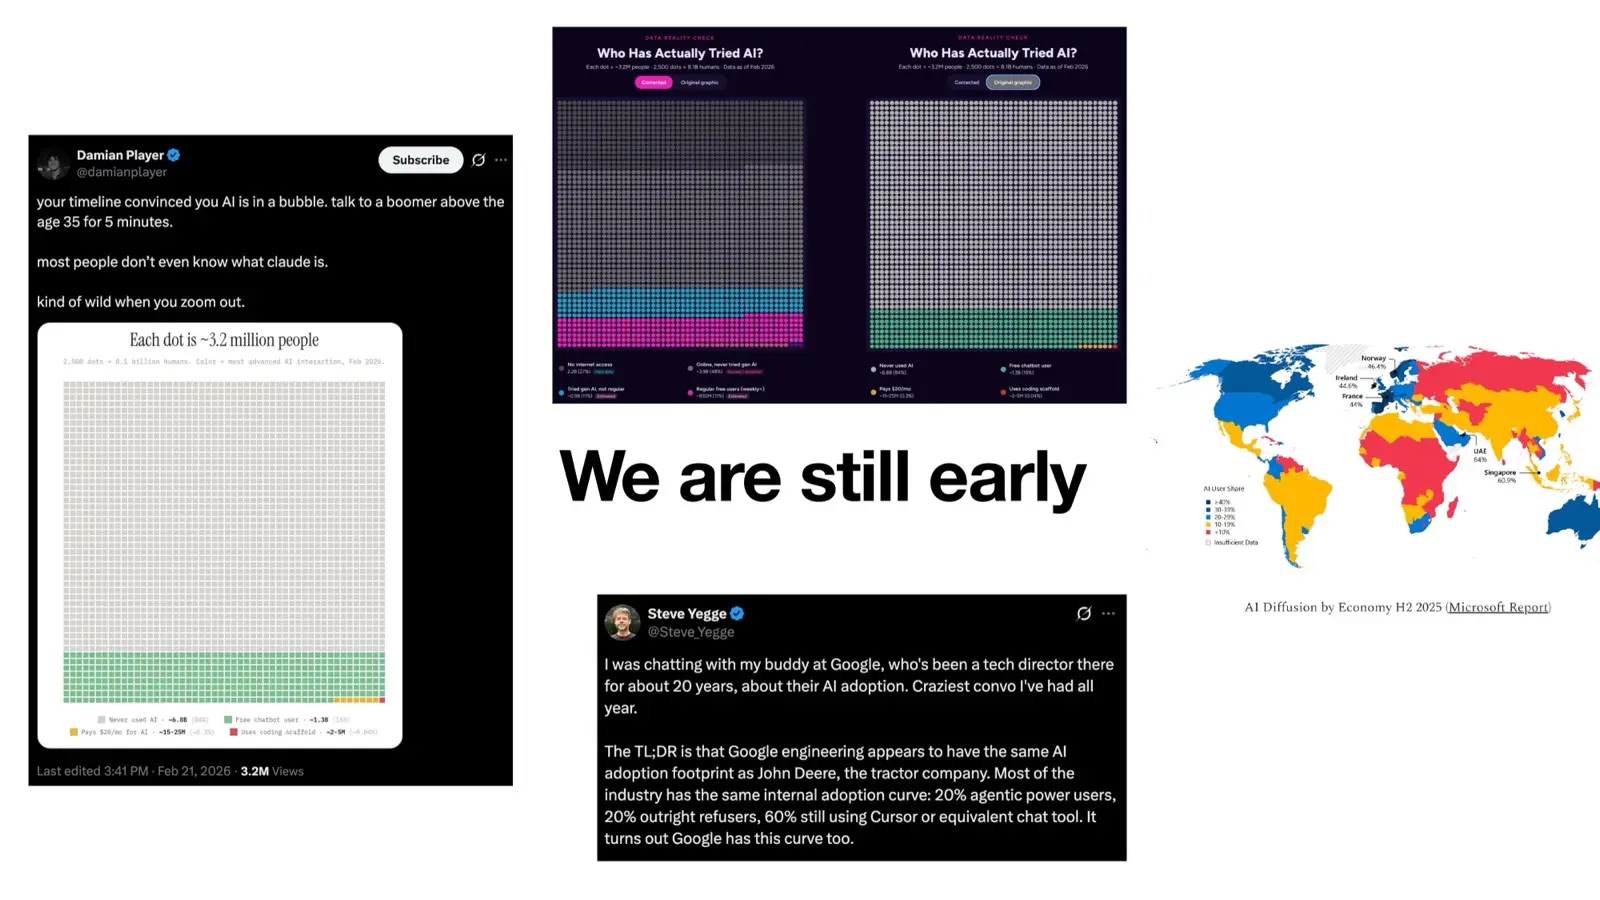
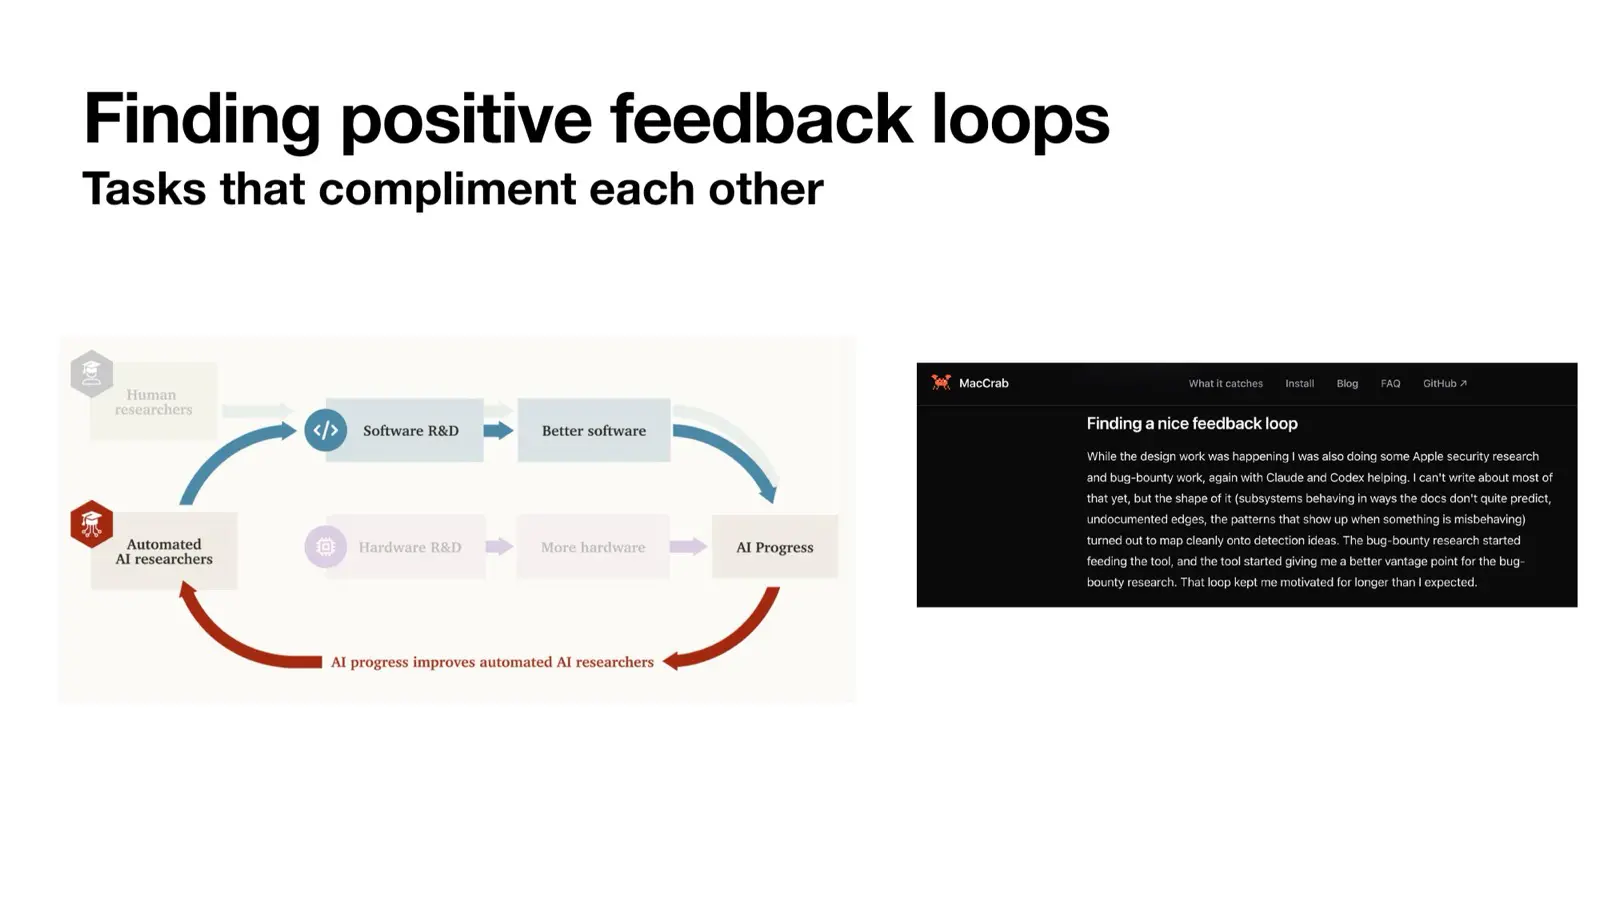
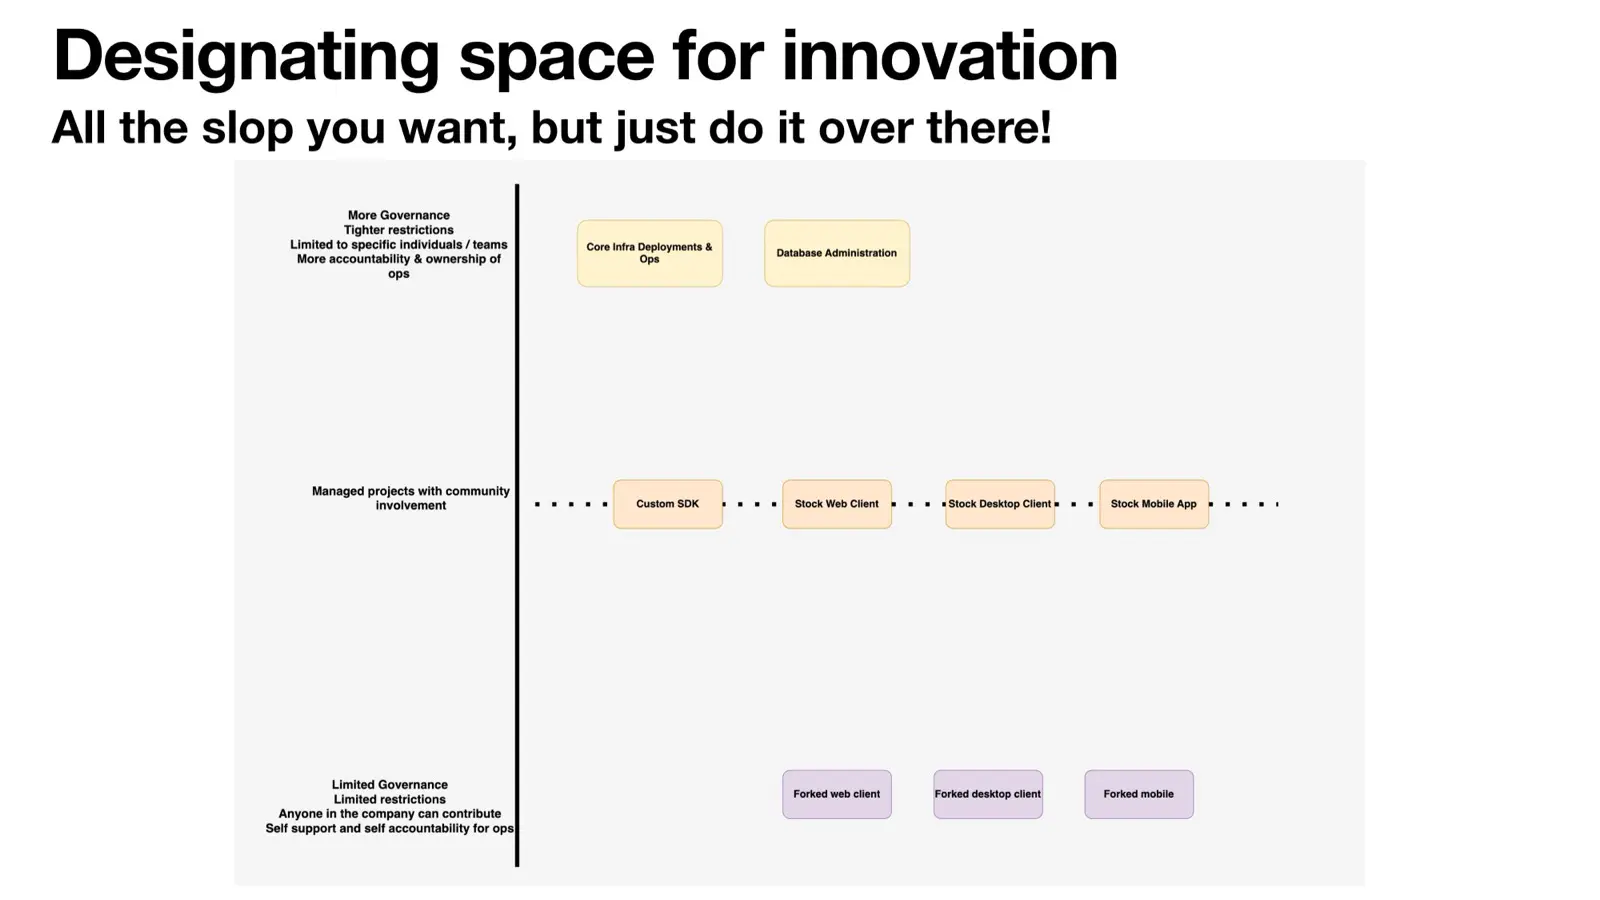
Whether we are early or late to AI matters less to me than what has become possible. Putting existing components together in new combinations and running small experiments can help answer that. The catch is that every experiment is more unfinished software to look after, so I argued for giving innovation its own space.
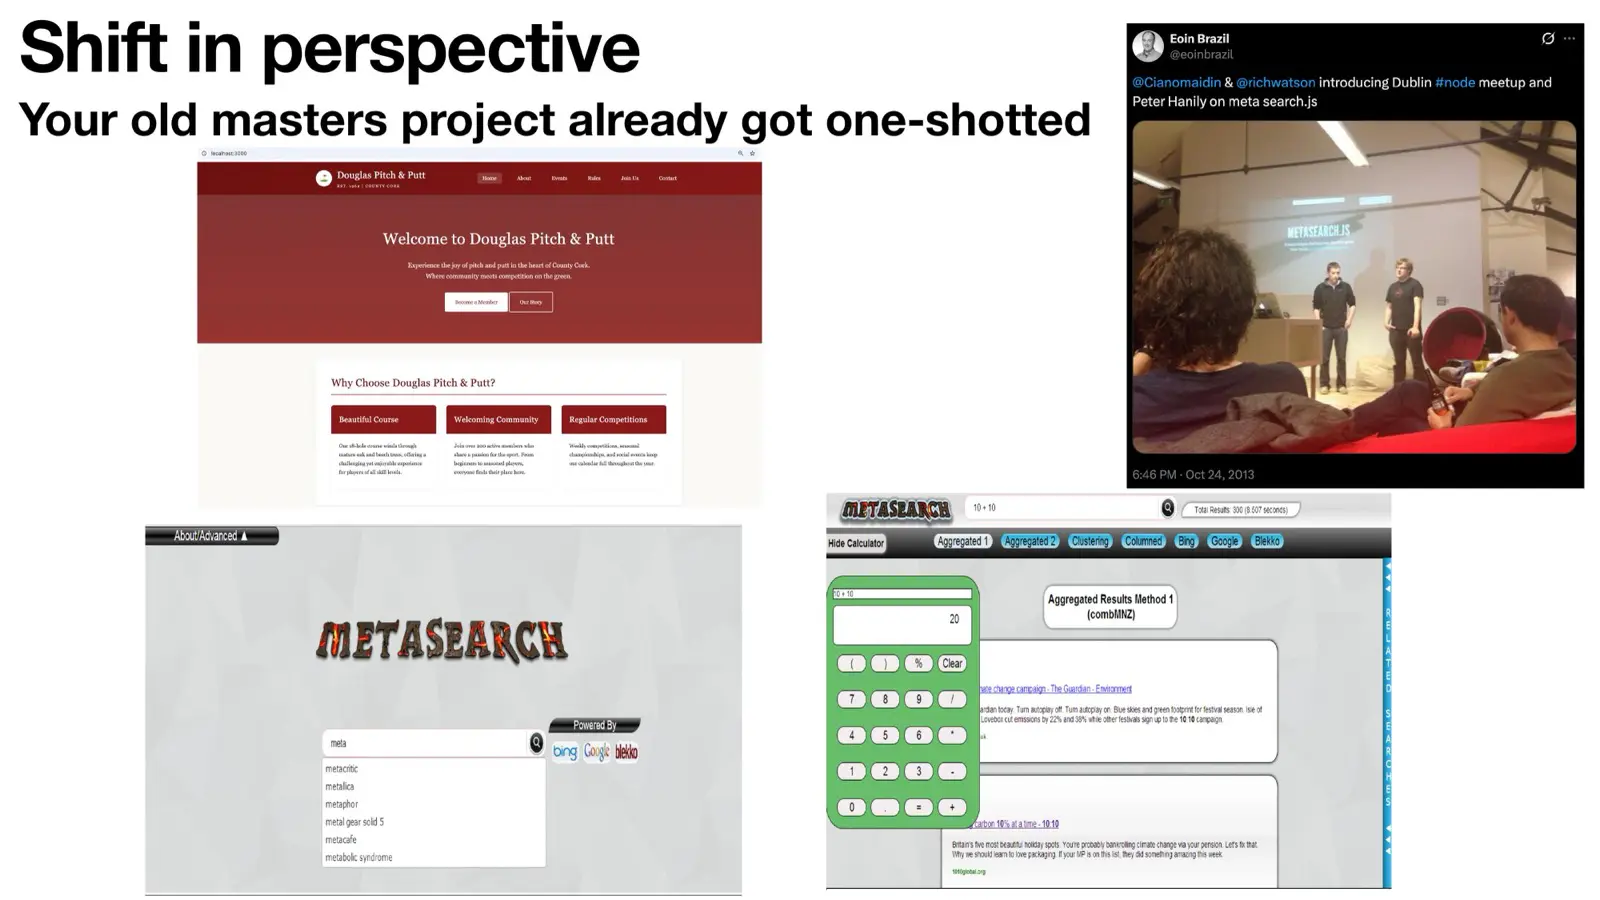
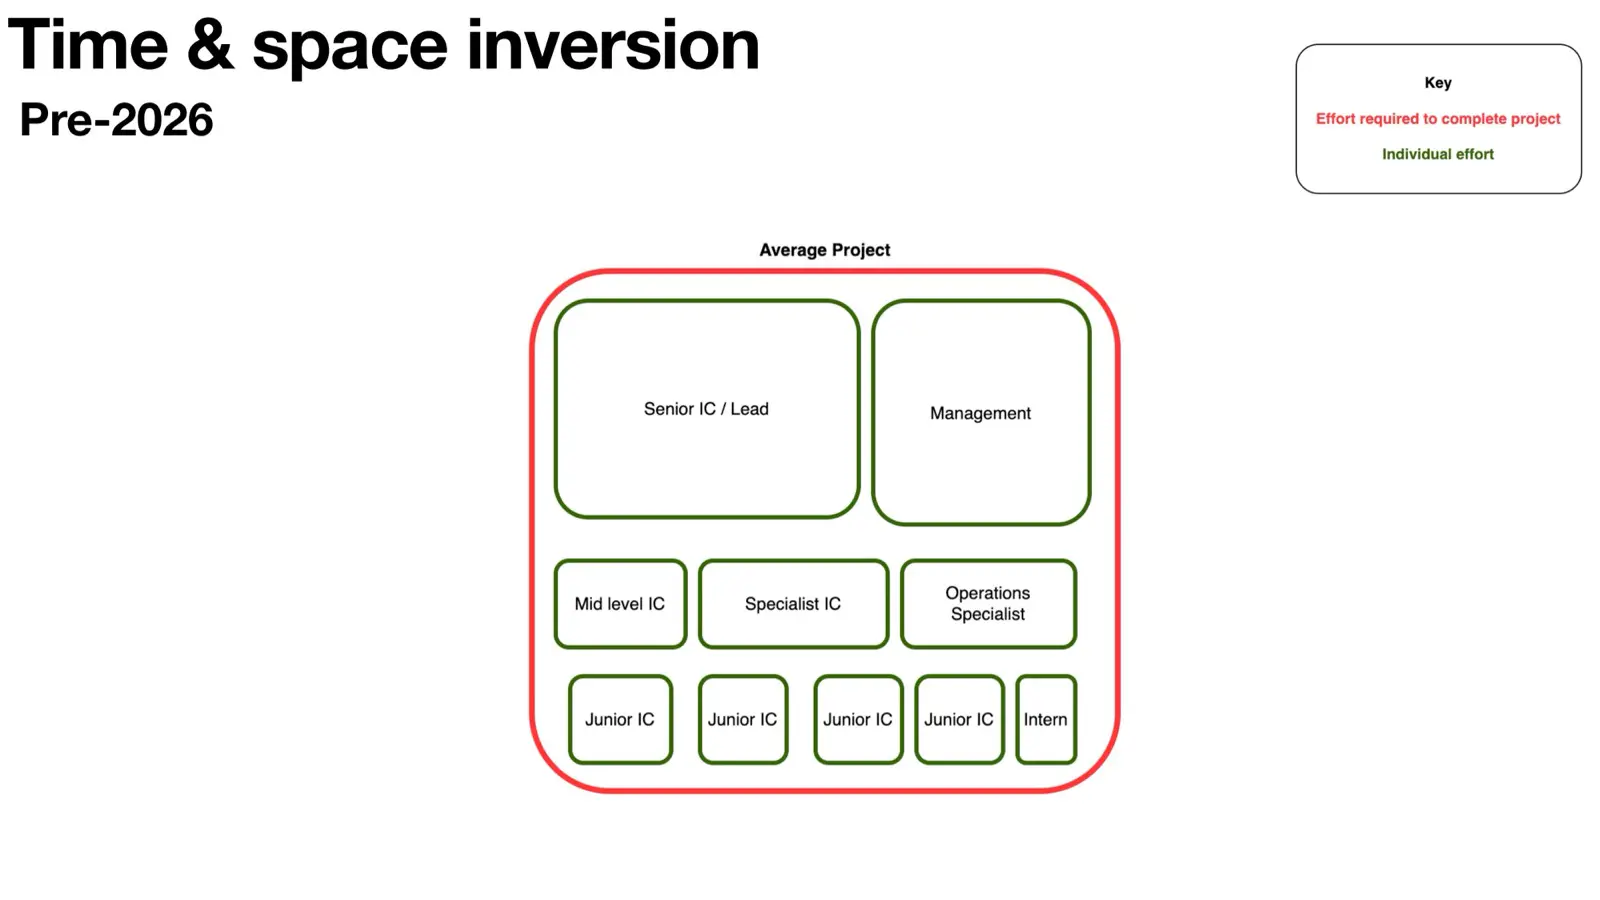
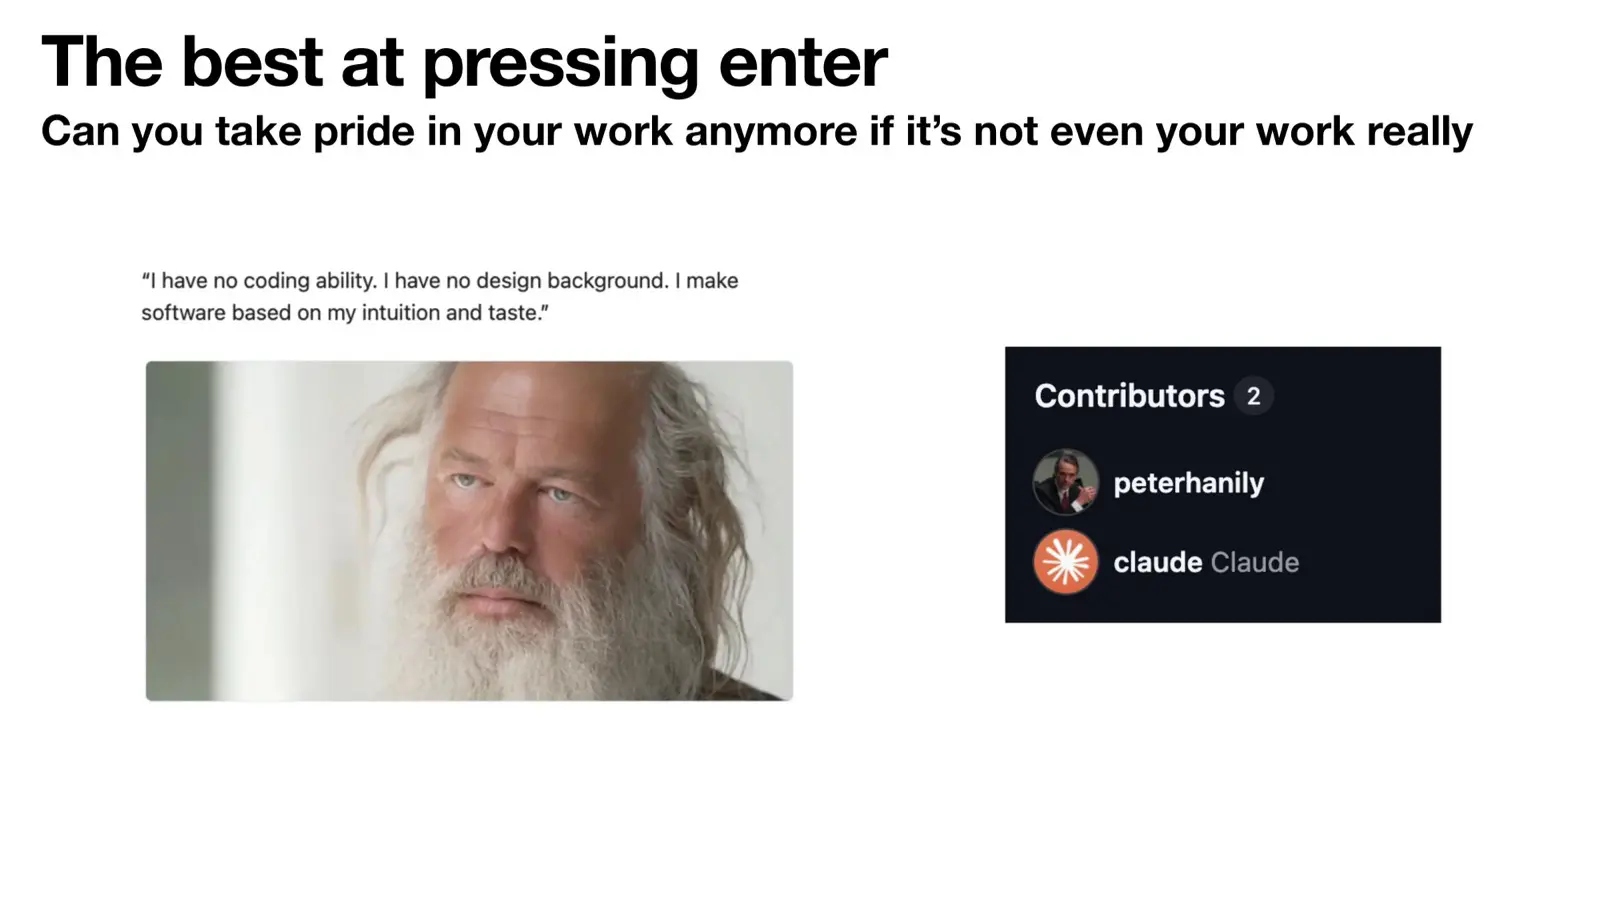
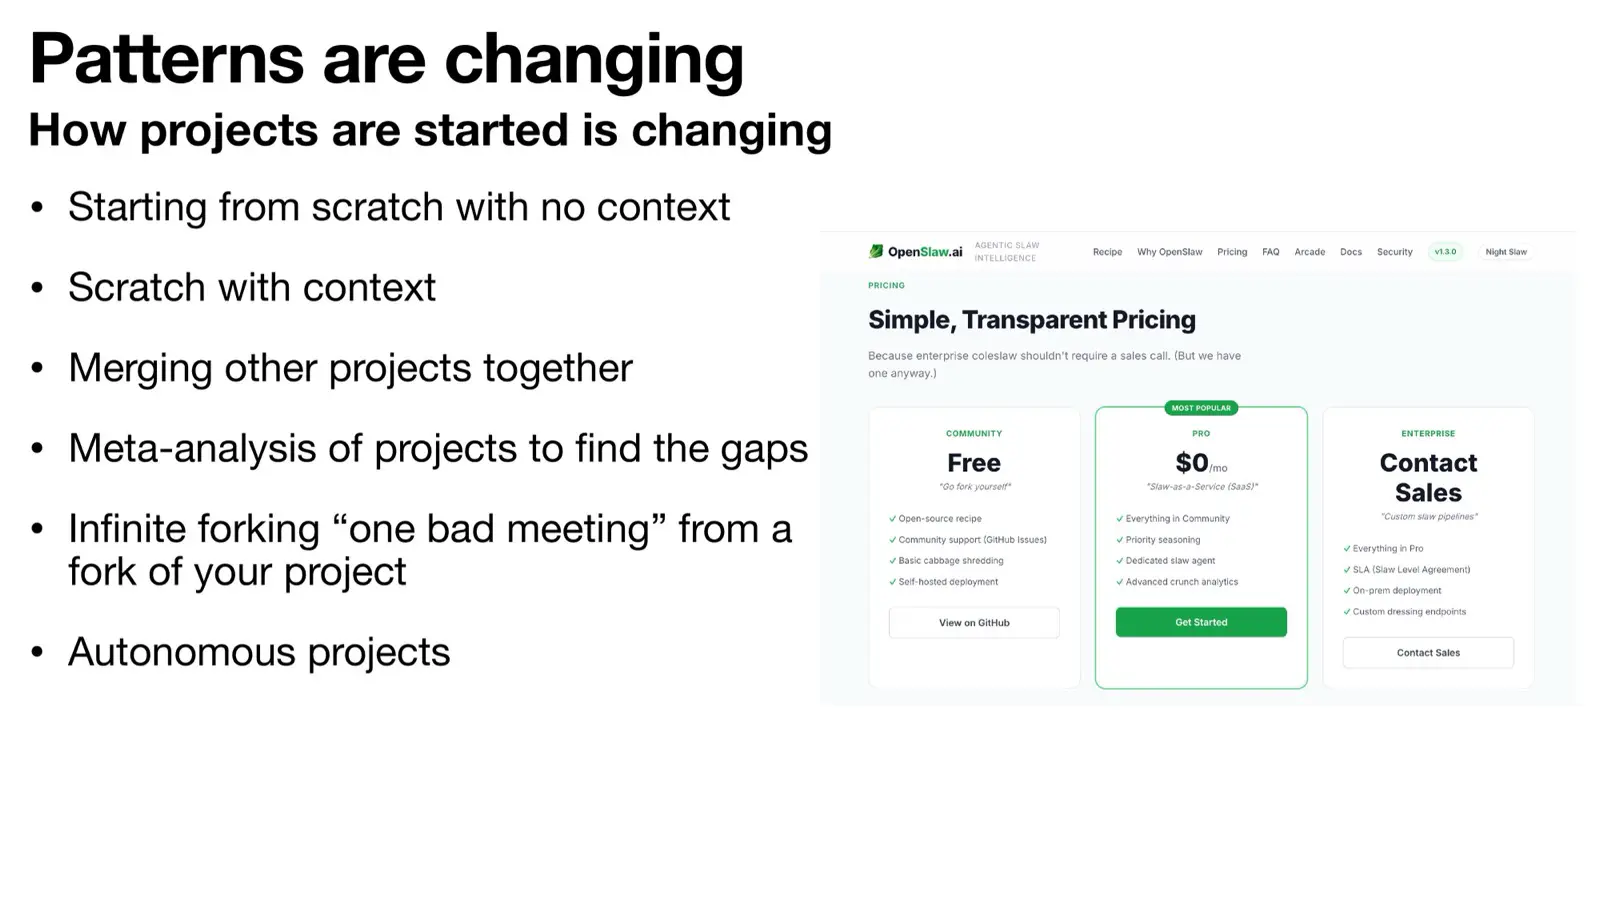
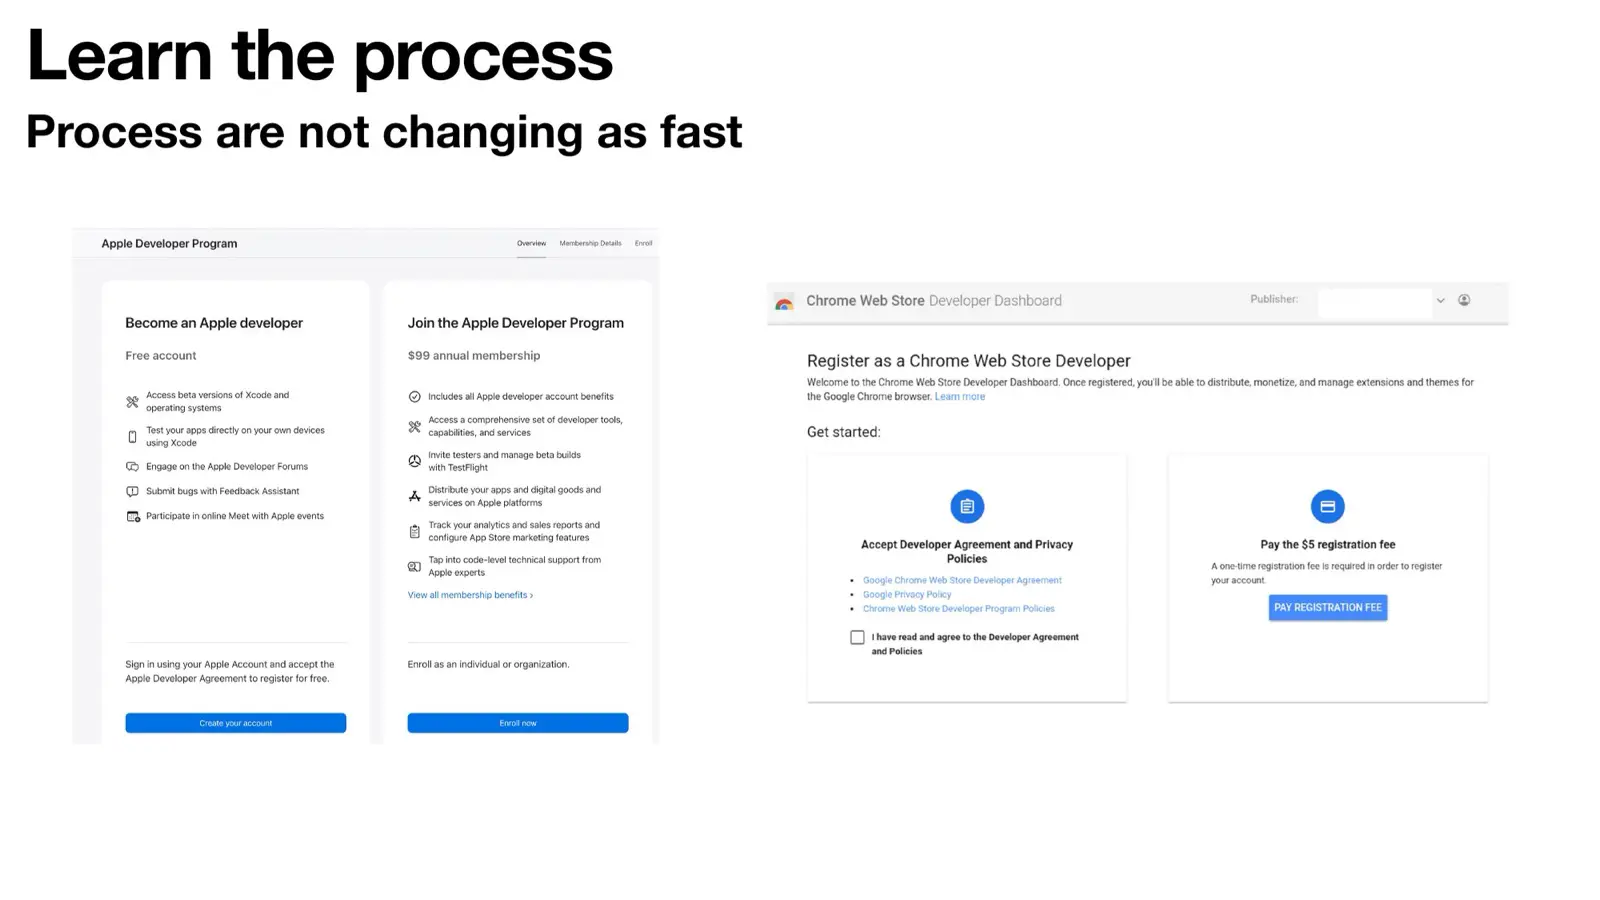
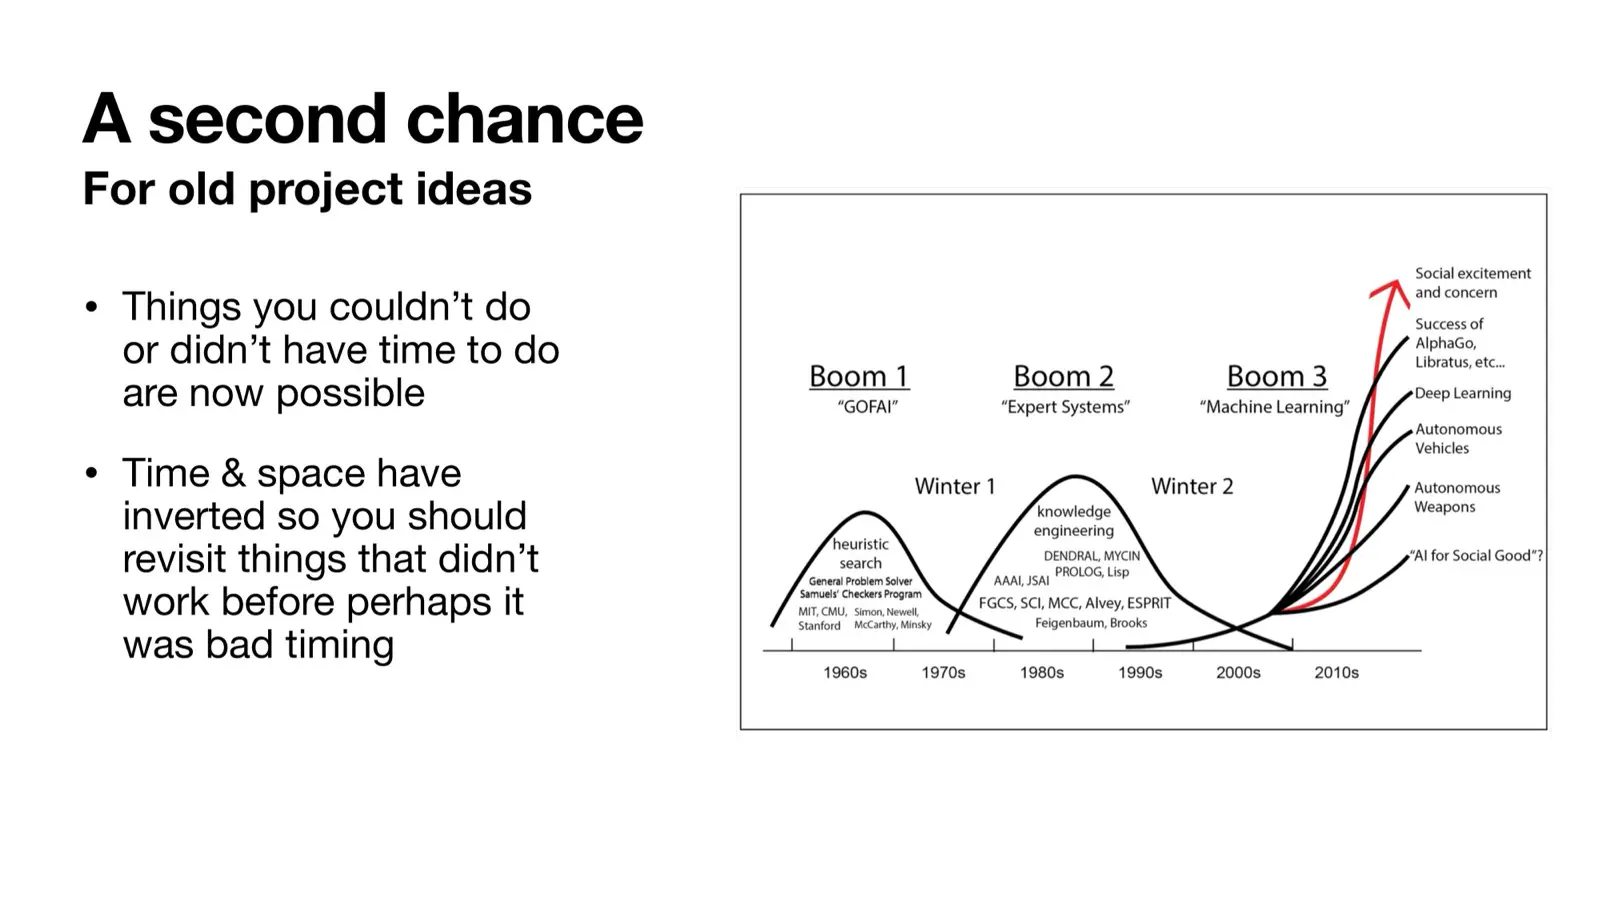
The advice I gave was to start with the person using the tool, and to name the task or decision you want to improve before choosing what to build. The next step is to learn the process around it. The way projects get started is changing faster than the processes around them, so a fast build is only useful when it fits how a team investigates, shares information and operates the result. The last is to give old ideas another look, especially the ones that lost out to time or cost, and to evaluate what comes out.
Max Clawdroom is what the Clippy argument turned into, and it was the second of the two demos in the talk.
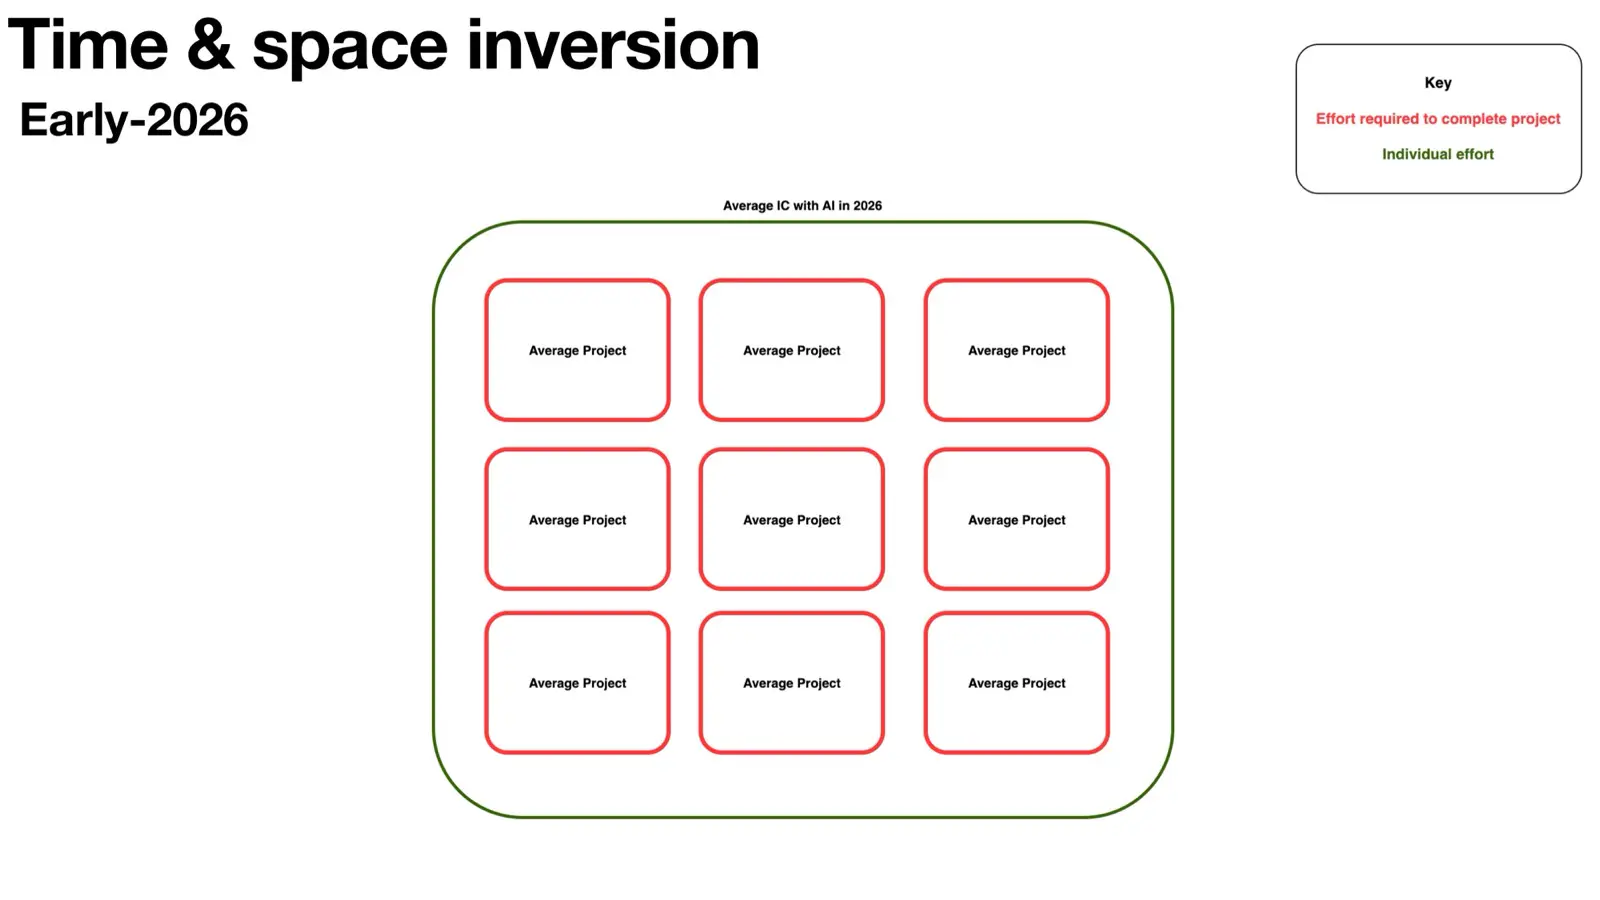
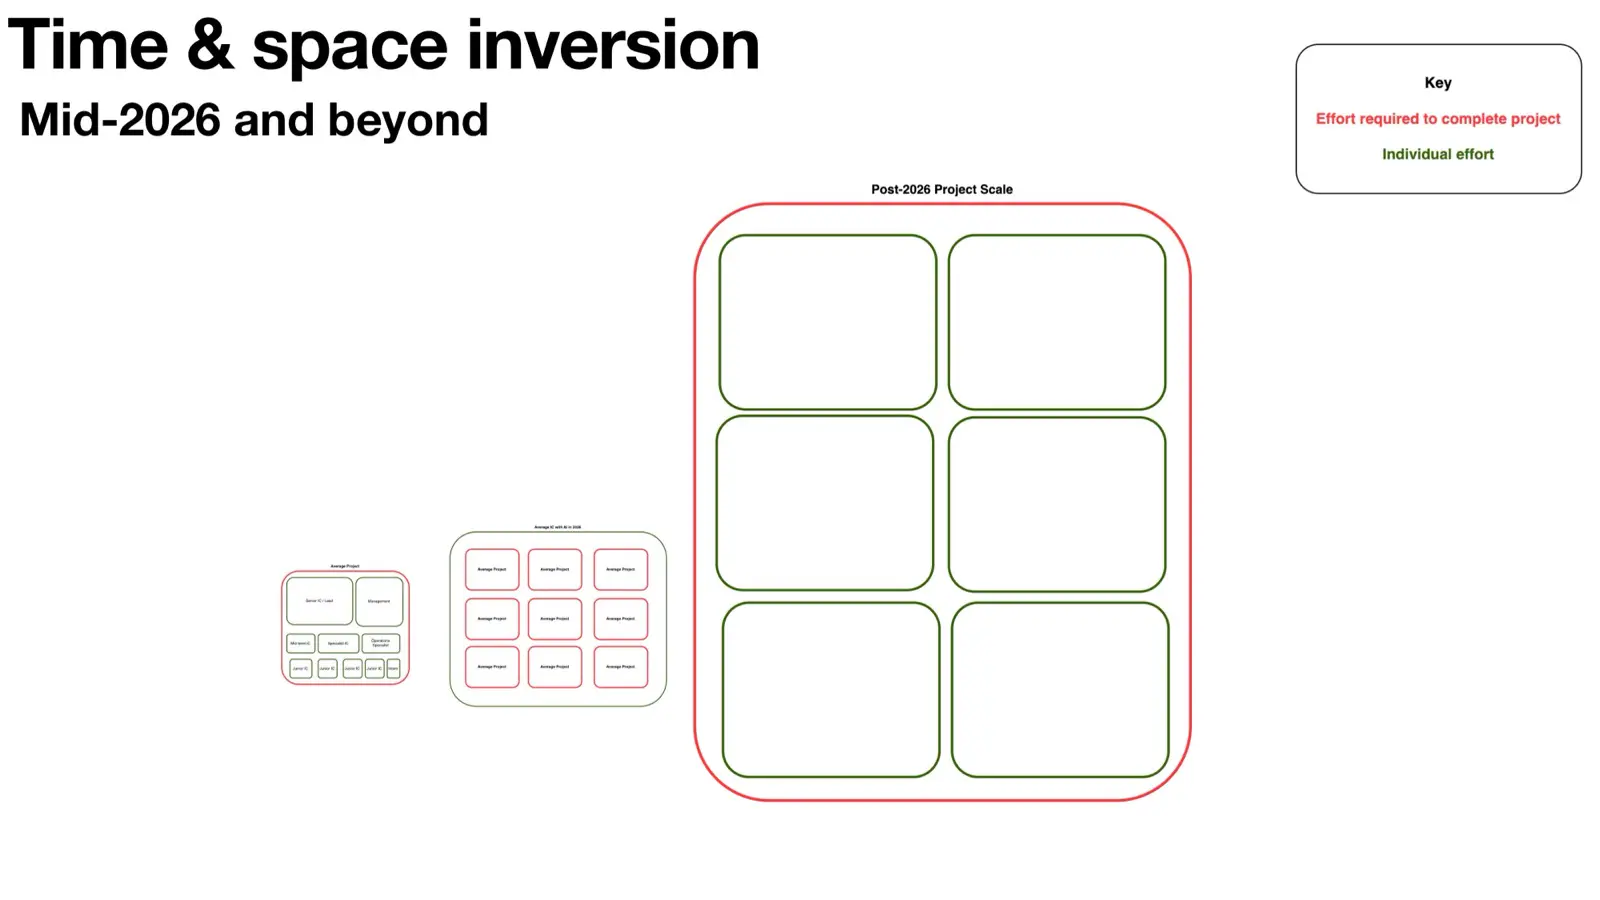
You can tell from how crude the slides are that I didn’t let AI build them. That was on purpose. There’s a story behind that decision I’m not going to spell out here; the deck can make the point on its own.
Download the complete slide deck. The section on who the tools are for begins on slide 15, and the Max demo appears on slide 30.
The pog
Too cheap for metal challenge coins, I printed the merch instead: a glow-in-the-dark “SecOps Reset” pog, designed with ChatGPT and run off a Bambu Lab printer. Attendees got one each.
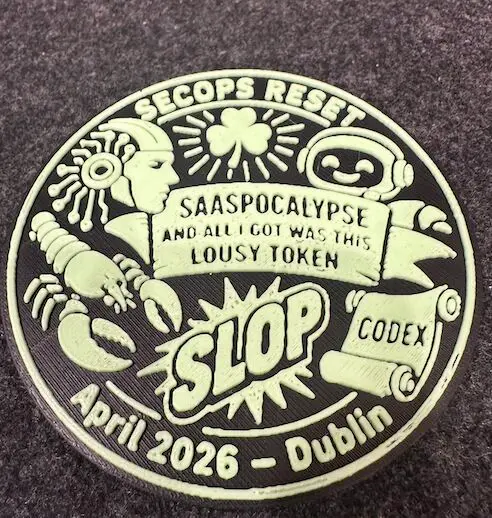
Attendees also got a first look at the desktop pet that came out of all this, Max Clawdroom, a native macOS companion for Claude Code. MaxClawdRoom is the new Clippy, we’re so back!
The rest of the day
It was a good lineup. Chetan Tibrewal spoke on multi-agent approaches in incident response. Cillian Collins and Ronan Donohue ran a CTF discussion that was one of the highlights, with a genuinely good argument that the security community would be further along if a fraction of the industry’s token budgets went to supporting and studying CTFs. That conversation is what pulled me back towards CTFs: it led to me getting involved with WICC and building CTFRadar a few months later. Athul Raju and I closed out the day with demos.
Thanks to Owen O’Connor for organising, and to everyone who came along. It was a great day and hopefully there’ll be another one in the future.